5 Effective HIPAA Breach Notification Letter Examples & Samples
Since HIPAA breach notification letters are a listed requirement required, it behooves every healthcare organization to prepare them as templates. Here are effective template examples.

39 breaches exposed over 1.5 million healthcare records due to breaches in 2020 alone.
That’s a jarring number regardless of which side of healthcare you’re on.
From the patient’s standpoint, you’re likely wondering how less than 50 companies have access to that many files. Something doesn’t add up.
On the facility side, your thoughts differ based on the time type of healthcare manager you are.
A passive manager wouldn’t think much of that statistic. They think that their compliance ecosystem is perfect and a breach couldn’t possibly happen to them. The proactive manager, though, understands the significance of that number. As a result, they reassess their cybersecurity and compliance policies. They also know that HIPAA breaches aren’t a matter of “if” they’ll happen, it’s a matter of “when”.
Obviously, after breaking down the two types of healthcare managers, I’m going to state that being on the proactive side of your cybersecurity and compliance practices is a must. But saying you’re proactive is one thing, actually incorporating the proper strategies is another.
Listing every compliance strategy that proactive healthcare managers incorporate into their organizations falls outside the scope of this blog post. You see, HIPAA breach preparation falls into three main categories…
- Pre-breach preparedness
- Incident response
- Post-breach activities
Pre-breach preparedness involves getting ready for what many cybersecurity experts view as the inevitable.
During this step, managers are ensuring that they’re compliant with all of HIPAA’s requirements, providing training to their workforce and putting into place the proper response protocol.
One of the often-overlooked aspects of the pre-breach preparedness step is creating HIPAA breach notification letter templates.
Although they’re required by the HIPAA Security Rule, they’re a bit of an ego check. What I mean by that is, some healthcare managers might feel that they’re better off ignoring the creation of these templates because creating them might feel like an admission of guilt.
But, since HIPAA breach notification letters are a listed requirement required, it behooves every healthcare organization to prepare them as templates. Here are effective template examples.
What's Required by Law
The HIPAA Breach Notification Rule is the specific portion of the law that requires this type of letter.
In a nutshell, it states that if something happens that leads to a breach in protected health information, the covered entity and/or business associate needs to tell those affected.
There are a few different types of notification that fall under this portion of the law including…
- Individual notice
- Media notice
- Notice to the Secretary
Individual and Secretary notice are both required, regardless of the size of the breach that occurs. Meanwhile, media notice only needs to happen if a HIPAA breach is 500 or more individuals.

The only real other takeaways from the Breach Notification Rule that fits within the scope of this blog post are the time limits associated with sending these notices…
- Individual Notice: 60 days following the discovery of the breach
- Media Notice: 60 days following the discovery of the breach and it affects 500 or more individuals
- Notice to the Secretary: 60 days following the discovery of the breach and it affects 500 or more individuals
Of course, there is some more important information required as a part of a breach notification but I’ll cover those aspects while going through examples.
Example 1: The True Template
The most effective strategy to incorporate as a part of your pre-breach preparedness activities is to create a HIPAA breach notification letter template.
This is one of the main concepts that I was trying to hint at during the introduction of this blog post. It’s also the step that some managers feel weary about incorporating, almost as if by creating a breach notification letter template they’re jinxing their organization.
This blog post exists to help you throw those superstitions and bolster your incident response plan.
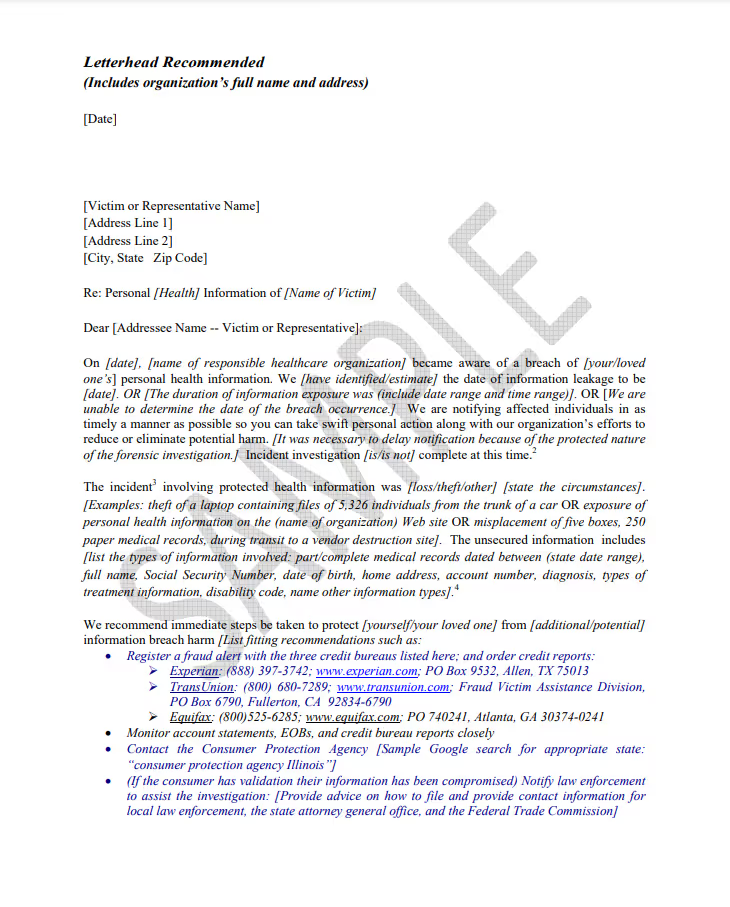
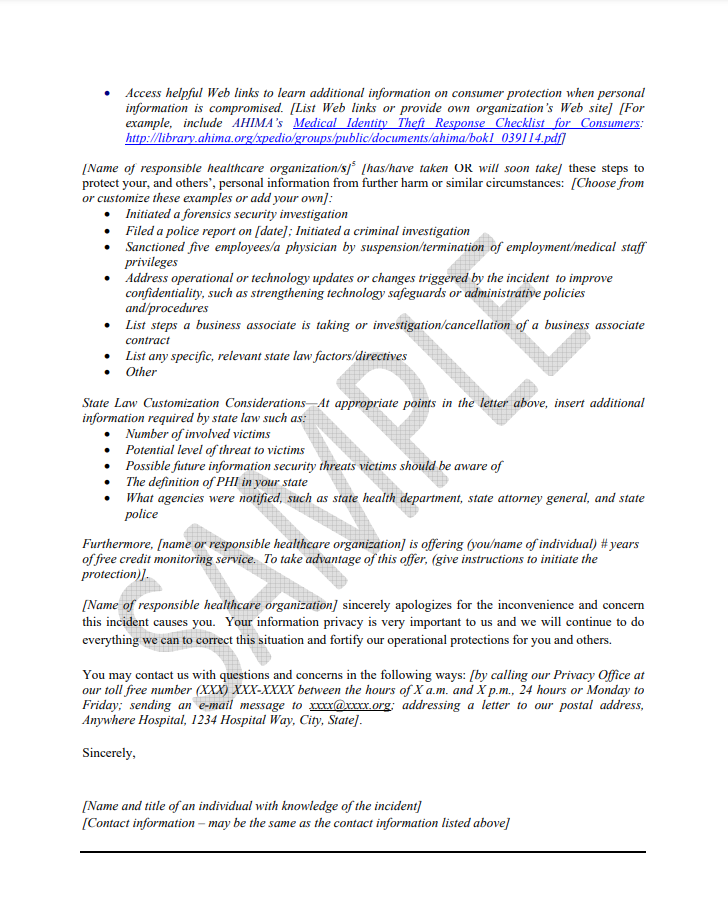
Anyway, the first effective HIPAA breach notification letter I have for you is a true template and it comes from the credible AHIMA organization.
What I mean by that is that it exists as a shell of what its final format would look like but contains placeholders throughout it. These placeholders make your incident response efforts easy.
If a HIPAA breach occurs at your organization, time isn’t on your side. It might seem like 60 days is plenty of time to draft a professionally formatted letter that informs your affected patients about what happened, but it really isn’t.
In that time you have to figure out exactly what happened, determine proper disciplinary actions if one of your employees is at fault and figure out which of your patients got exposed.
All of that information also needs to exist within the notification letter that you sent out. After all, if you breached your patient’s sensitive information you need to be crystal clear about exactly what happened.
Thus, a template notification letter allows you to plug in all of the necessary information in an effective, predetermined format to save you time and ensure that you meet the limit.
Example 2: The Website Notice
As I promised in the section about what’s required by HIPAA, it has more requirements based on different scenarios that covered entities may find themselves in.
For this section, I’m specifically referring to the website notification.

You see, the HHS requires that if a covered entity doesn’t have accurate contact information for 10 or more clients, they need to provide notice on their website or utilize another form of public media.
There are multiple ways to accomplish this type of notification letter, but the best way is by providing the details within a devoted webpage.
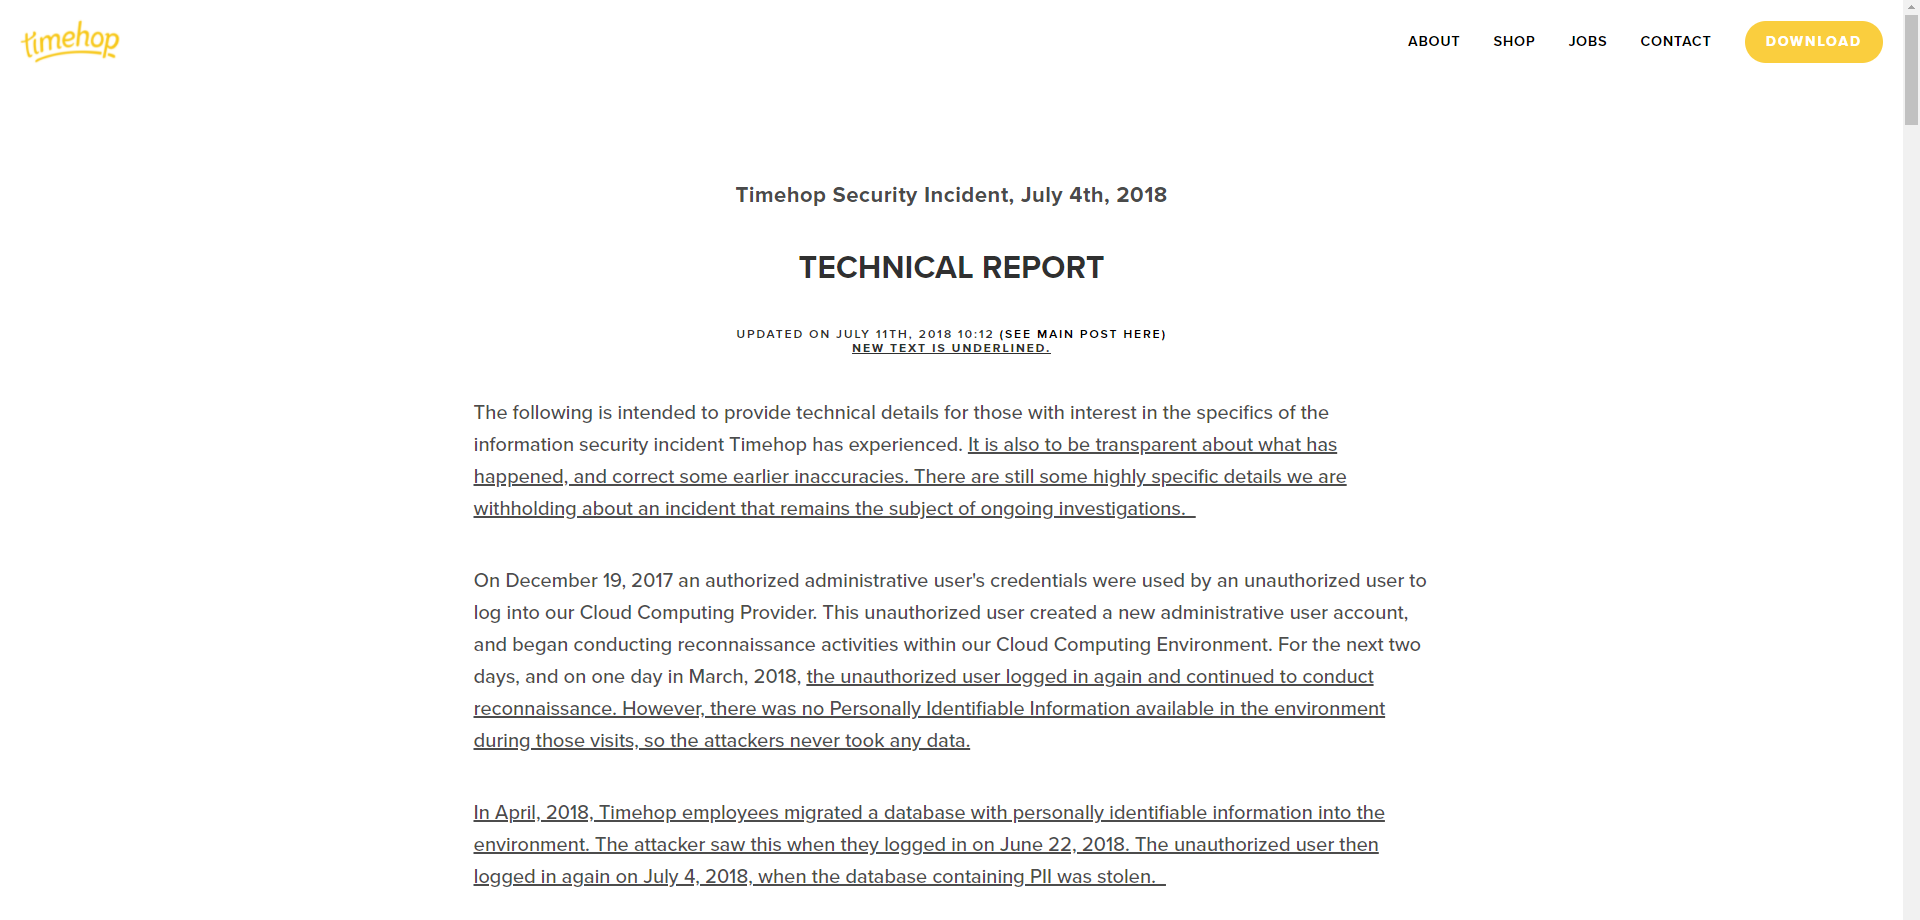
This next example comes from a security incident that Timehop experienced in 2018. Before I go any further, I know what you’re thinking, “This example isn’t a HIPAA violation.”
Although you’re correct on that, focus on the format itself.
You see, Timehop’s notification letter is a perfect example of what it should look like on your website if you experience a breach.
Of course, the content provided is going to be different. But if you created a template letter similar to example 1, all you have to do is copy and paste it into an electronic format.
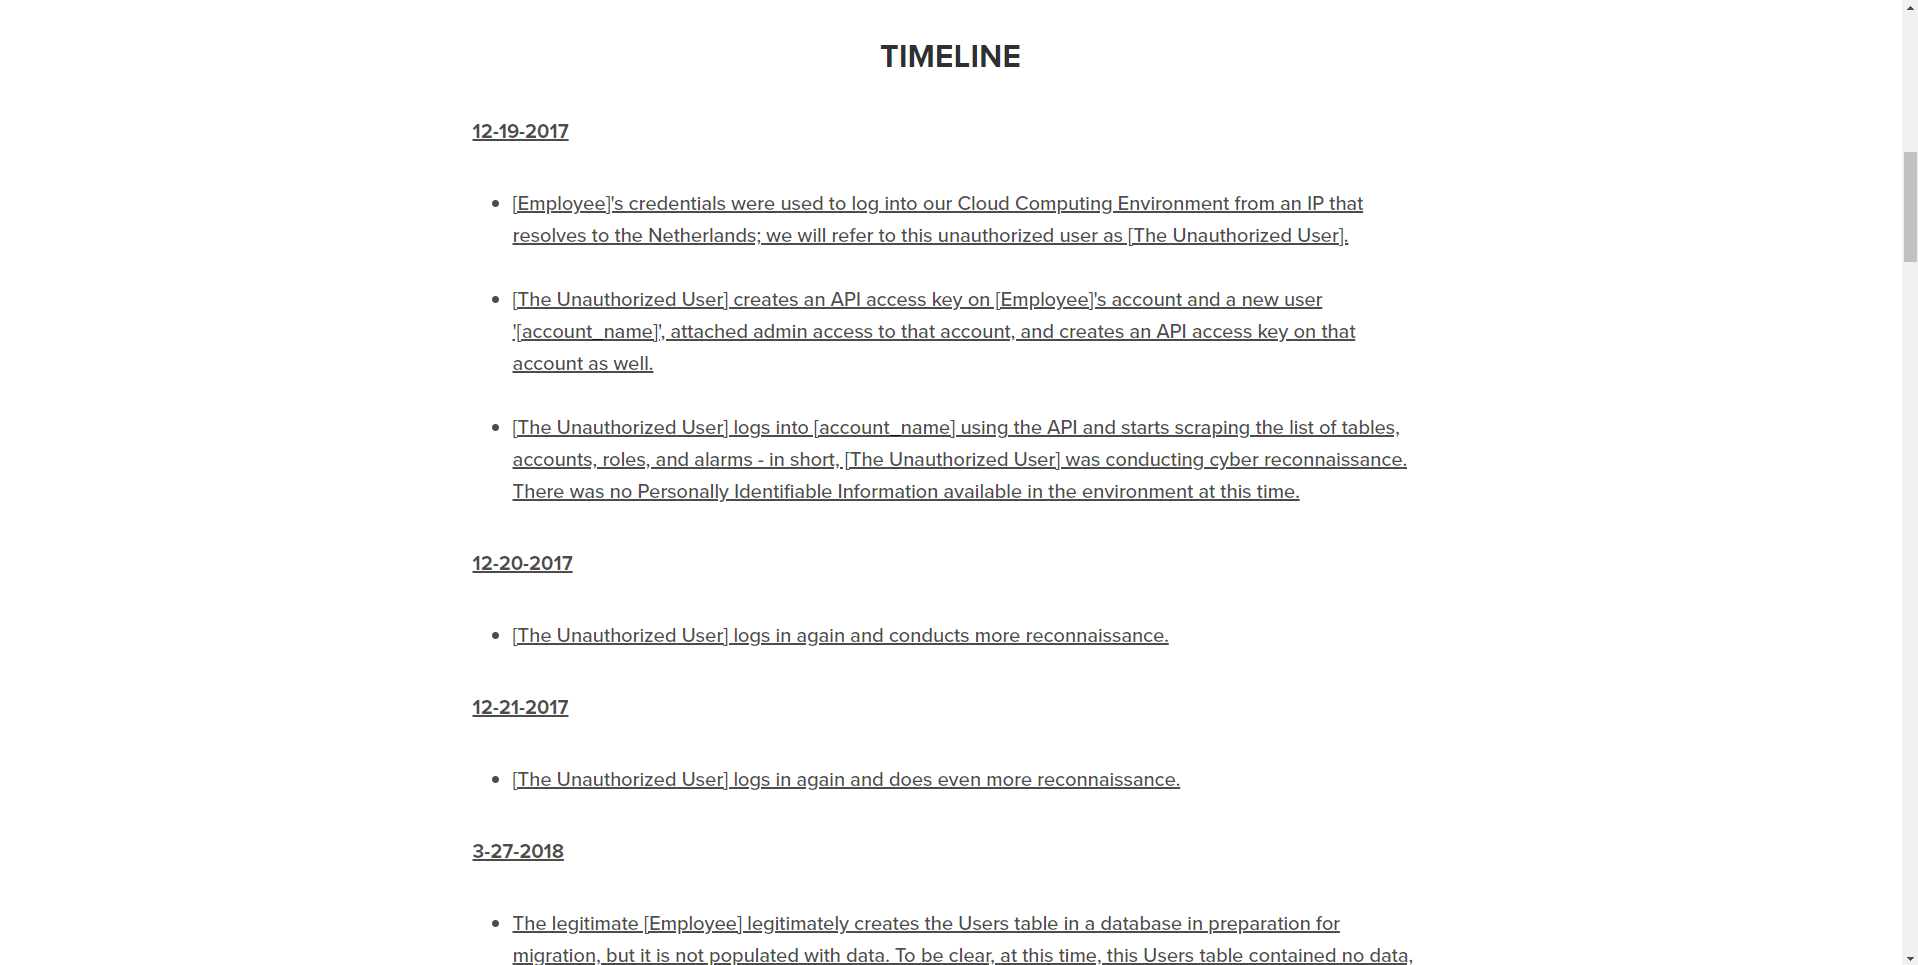
Timehop gets bonus points for including a daily timeline that explains the events that occurred during their security incident.
Example 3: The Social Media Notice
With how younger generations prefer their healthcare experience, it wouldn’t be a surprise if your healthcare organization sees more activity on the social web than on its website.
If that scenario describes you, then posting a social media notice regarding your breach is a must.
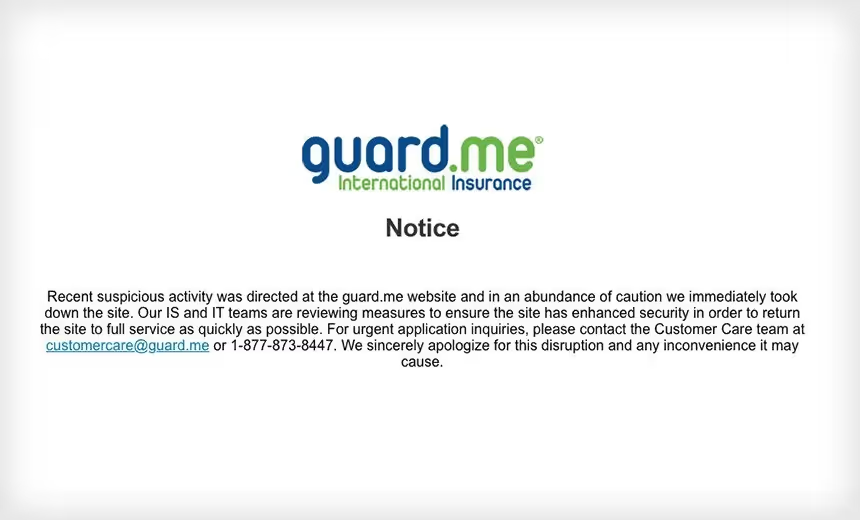
Guard.me provided a great example of a breach notification letter that’s formatted for digital sharing.
I said “digital sharing” because the notification you post about on social media shouldn’t be exclusive to those platforms. You can also include a well-formatted image announcement in your email newsletter.
If you do choose to or have no choice but to make a digital announcement regarding a HIPAA breach, you should include text AND imagery in what you share. After all, social media posts that include an image receive 2.3 times more engagement than those that don’t.
Since HIPAA requires that you alert your patients when a breach happens, you will want as much engagement as possible to avoid a fine from the HHS.
Example 4: The Email Notice
Since we know that many patients now prefer paperless billing, it’s safe to say that they’re active on their email accounts.
You see, in most cases, paperless billing means that the notification gets sent via email. So if your patients are already receiving billing communications from you, it makes sense to inform them of any breaches in the same way.
I kind of hinted at this section in the previous one, but what I wrote was more so for those healthcare organizations that send newsletters. Although newsletters are a great way to engage with patients, the facilities that implement one are in the minority.
Whether you do or don’t is irrelevant, though, because a full-fledged breach notification letter sent via email looks different than the shareable image from the section above.
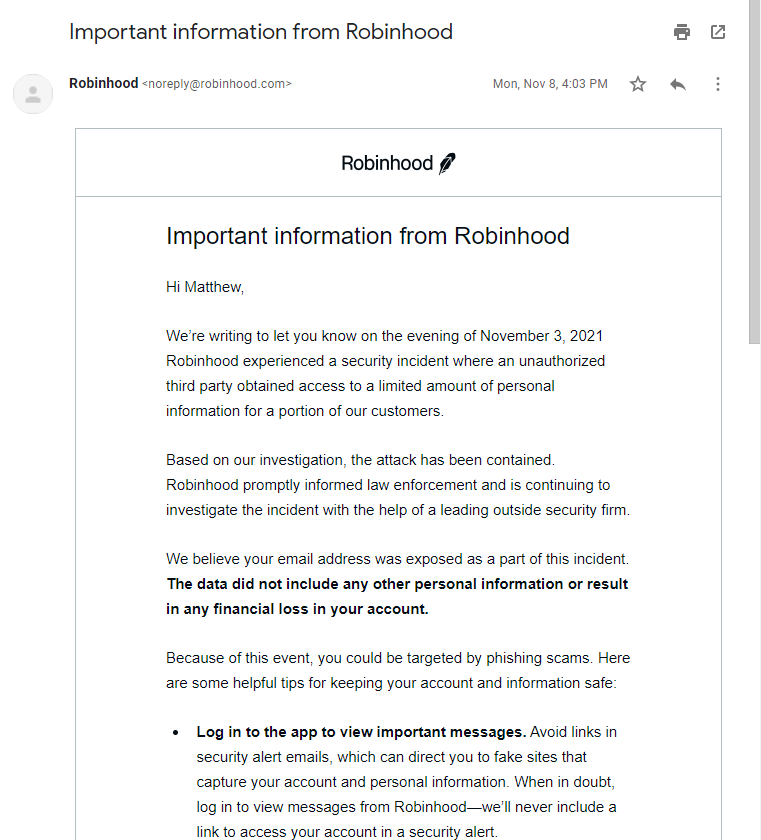
The example image above is a security breach notification letter received by the stock trading company, Robinhood.
As you can see, the email isn’t a graphical masterpiece…and it doesn’t have to be.
When a breach occurs in any capacity, the only things that those affected care about are…
- What happened
- Was my information affected
- How can I protect myself
A pretty image isn’t going to provide all of that information and acts as more of a distraction than anything else.
Instead, provide a thorough explanation for each area that your patients care about knowing.
Example 5: Phone Call and Voicemail
The last available option you have isn’t technically a letter, but you might still find yourself in a scenario where it’s your only breach notification option.

You see, part of the HIPAA Breach Notification’s requirements is to include a toll-free phone number. It needs to stay active for at least 90 days. It’s practically the same requirement from earlier regarding public websites and media postings.
I’ll admit that leaving a HIPAA-compliant voicemail is an entirely different animal. But a breach notification voicemail is a little bit different. In this case, you can inform your affected patients without giving any compromising information over the phone.
All you and your team have to do in this case is give your patients a call and tell them what happened, explain what’s at risk and what they can do to find out if they were a victim.
Conclusion
After reading this blog post you definitely know that notifying your patients that you experienced a HIPAA breach is a requirement (in case you didn’t before).
However, understanding that that is a requirement placed on your organization isn’t the hard part. It’s figuring out the best way to do it and having a plan in place BEFORE the breach occurs that’s difficult.
Of course, even after I’ve listed all of these different effective examples to notify your patients of a breach…you likely still have one question remaining, “What is the most effective one?”
The answer to that question is to use a mix of all of them. Cover your bases by communicating what happened effectively, across multiple platforms and mediums.
Emphasize your product's unique features or benefits to differentiate it from competitors
In nec dictum adipiscing pharetra enim etiam scelerisque dolor purus ipsum egestas cursus vulputate arcu egestas ut eu sed mollis consectetur mattis pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus mauris aliquam ornare nisl purus at ipsum nulla accumsan consectetur vestibulum suspendisse aliquam condimentum scelerisque lacinia pellentesque vestibulum condimentum turpis ligula pharetra dictum sapien facilisis sapien at sagittis et cursus congue.
- Pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus.
- Justo urna nisi auctor consequat consectetur dolor lectus blandit.
- Eget egestas volutpat lacinia vestibulum vitae mattis hendrerit.
- Ornare elit odio tellus orci bibendum dictum id sem congue enim amet diam.
Incorporate statistics or specific numbers to highlight the effectiveness or popularity of your offering
Convallis pellentesque ullamcorper sapien sed tristique fermentum proin amet quam tincidunt feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
Use time-sensitive language to encourage immediate action, such as "Limited Time Offer
Feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
- Pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus.
- Justo urna nisi auctor consequat consectetur dolor lectus blandit.
- Eget egestas volutpat lacinia vestibulum vitae mattis hendrerit.
- Ornare elit odio tellus orci bibendum dictum id sem congue enim amet diam.
Address customer pain points directly by showing how your product solves their problems
Feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
Vel etiam vel amet aenean eget in habitasse nunc duis tellus sem turpis risus aliquam ac volutpat tellus eu faucibus ullamcorper.
Tailor titles to your ideal customer segment using phrases like "Designed for Busy Professionals
Sed pretium id nibh id sit felis vitae volutpat volutpat adipiscing at sodales neque lectus mi phasellus commodo at elit suspendisse ornare faucibus lectus purus viverra in nec aliquet commodo et sed sed nisi tempor mi pellentesque arcu viverra pretium duis enim vulputate dignissim etiam ultrices vitae neque urna proin nibh diam turpis augue lacus.