HIPAA Training Requirements for Employees by Topic
Someone who’s in charge of creating a training regimen for their staff needs to incorporate all necessary topics to cover their bases so they prevent a breach. If you only cover part of HIPAA laws, regulations, and related requirements, then you could face serious consequences in the future.
The Health Insurance Portability and Accountability Act doesn’t only apply to nurses and doctors. Anyone that handles medical records, such as clearinghouse employees, needs to receive HIPAA training.
If isn’t properly administered, employees are likely to breach the HIPAA laws and regulations outlined by the U.S. Department of Health and Human Services (HHS). After all, how are you supposed to know when they can disclose protected health information (PHI) or who to share it with? Depending on the severity of a breach, it could lead to civil or criminal lawsuits.
If you work for a covered entity, then hopefully by now you’ve received some type of mandatory training by your employer. But just because you participated in something doesn’t mean that you’re familiar with every way to handle PHI and keep it safe.
Someone who’s in charge of creating a training regimen for their staff needs to incorporate all necessary topics to cover their bases so they prevent a breach. If you only cover part of HIPAA laws, regulations, and related requirements, then you could face serious consequences in the future.
Making your team read every single word of these laws isn’t the best solution. There’s no way they could remember or even understand all of those details, especially with how complex the regulations are. Instead, comprehensive and detailed courses are a much more effective way of teaching employees about HIPAA.
So what information do you include? Below are ten different topics and ideas to follow so that your organization meets HIPAA training requirements for employees.
Who's Affected By HIPAA?
I mentioned already that anyone who deals with medical records and information must adhere to HIPAA. It specifies who needs to follow its standards and regulations.
All of those who need to follow HIPAA laws must also complete training so that they know how to follow the regulations. Understanding who it applies to is the first step to making sure that your organization’s employees meet the requirements.
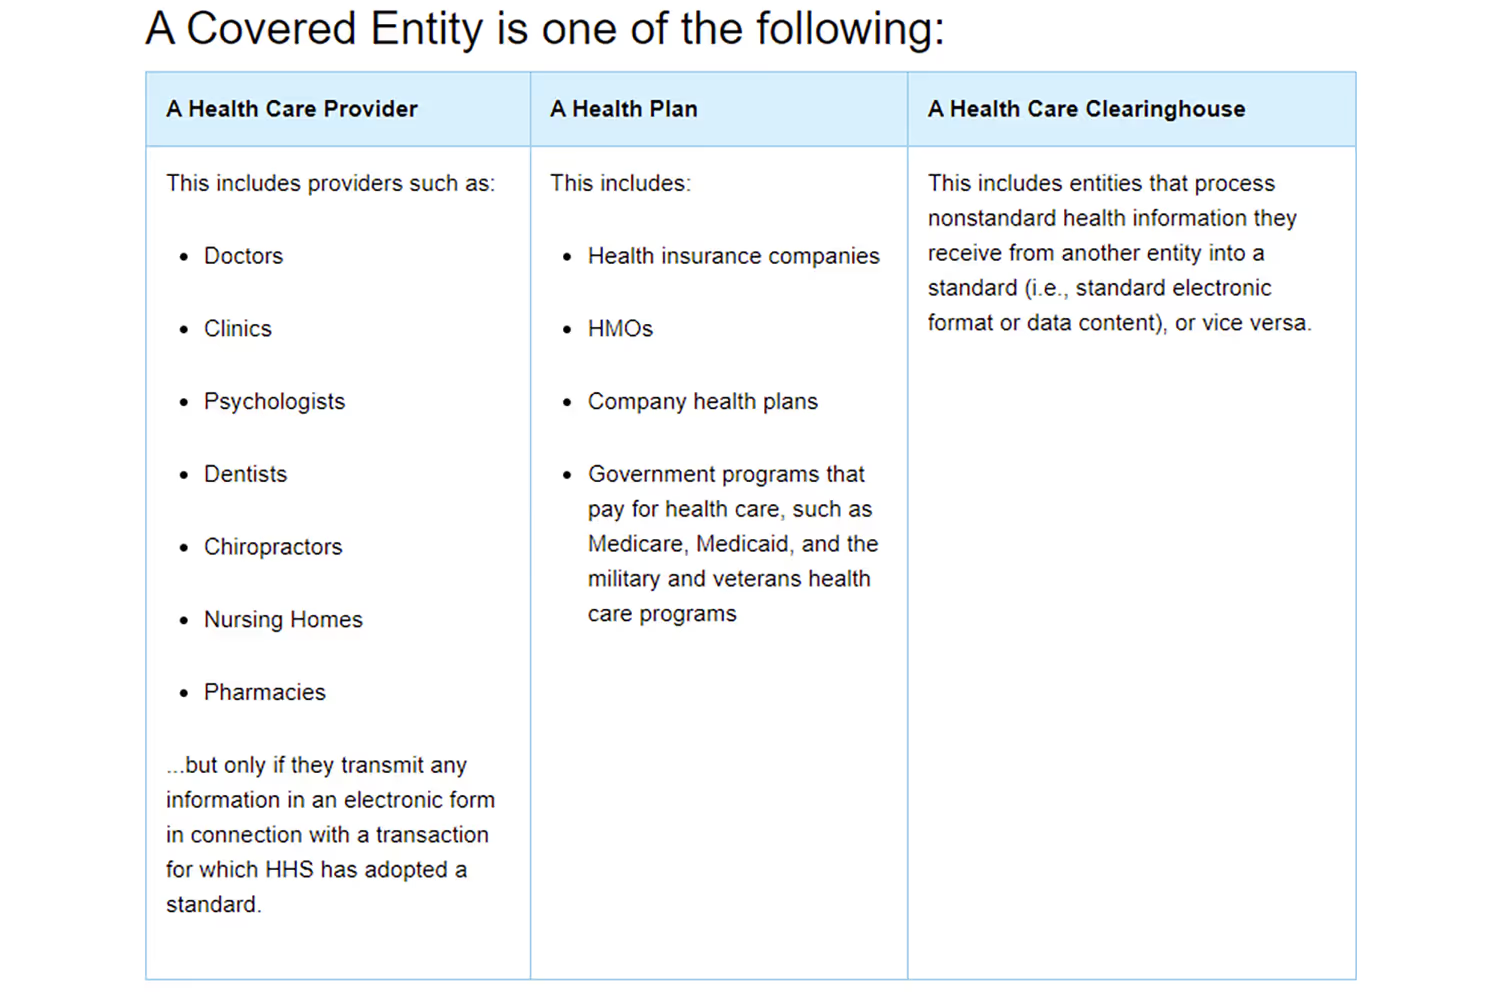
HIPAA rules apply to covered entities and business associates. Covered entities include healthcare providers, health plans, and healthcare clearinghouses.
More specifically, these are…
So then what are business associates, and how does this law apply to them?
These are organizations that help the covered entity carry out its healthcare functions. Most covered entities don’t conduct all of their functions on their own.
If they rely on an outside business, then they need to have a written business associate agreement (BAA) that…
- Establishes the tasks that the business associate must do once hired
- Requires the business associate to comply with HIPAA Rules to protect PHI
This contract makes the business associate liable for compliance as well. Some organizations won’t sign a BAA because they don’t want that kind of liability. If that’s the case, then the covered entity would have violated the HIPAA Privacy Rule for disclosing PHI without an agreement that the person or entity would safeguard that data.
The only entities that don’t need to comply with HIPAA Rules are those that don’t meet the definition of a covered entity or business associate.
Covering Your Bases
Because there’s so much information within this law, it’s helpful to break up topics into different modules. If you do this, you can include an initial training module that covers basic information about the law.
Essentially, this section should go over general details that any employee would need to know, regardless of their role. What is HIPAA, and what’s its purpose? Who does the law apply to and what are its objectives? This gives employees a general understanding before overwhelming them with more specific details.
It’s also useful to define what the Privacy Rule and Security Rule are. These rules set the national standards for protecting patients’ health information. Of course, each of these has many standards, so it’s still helpful if they each have their own training modules as well.
Since it’s best to break up topics into sections, you don’t want to get too technical about certain terms yet. Rather, you can go over terminology from a high-level overview. That way, your employees have some background information when they get to the more specific training topics.
HIPAA Privacy Rule
One of the first modules administered to employees of a covered entity should cover the Privacy Rule. It applies to health plans, health care clearinghouses, and healthcare providers that deal with electronic PHI (ePHI).
The Privacy Rule requires the implementation and maintenance of appropriate safeguards to protect data. It also sets standards concerning permitted uses and disclosures of PHI. This Rule stipulates when it’s necessary to obtain written consent from a patient to disclose this data.
Furthermore, it outlines patients’ rights to their PHI. Individuals have the right to…
- Examine their health records
- Obtain copies of these records
- Direct a covered entity to transmit their PHI electronically to a third party
- Request corrections
HIPAA Security Rule
The Security Rule is the next important topic to cover.
The technical, administrative, and physical safeguards of this Rule impact every employee’s day-to-day activity, especially their electronic activity. Because of this, all employees of covered entities and business associates must receive training on the Security Rule.
Some important parts to include are…
- Procedures for guarding against, detecting, and reporting anything that looks like it could be malware
- Procedures for monitoring log-in attempts and reporting discrepancies
- Procedures for creating, changing, and safeguarding passwords
- Any updates to the rule
It should also include any protocols that the entity has implemented to prevent, detect, contain, and correct security violations. Therefore, the module covering the Security Rule should be specific to the organization that’s implementing and requiring the training.
Other topics relevant to the Security Rule that would be useful to cover within their own modules include:
- Different types of malware and how to identify and prevent them
- Ransomware prevention
- Incident response plans
- Cybersecurity awareness
- Examples of companies falling victim to cybersecurity breaches
The HITECH Act
The Health Information Technology for Economic and Clinical Health Act (HITECH Act) covers topics relevant to electronic health information and its supporting technology. The Act addresses the privacy and security concerns associated with the sharing of ePHI.
Training on the HITECH Act should cover the four categories of violations, each reflecting a higher level of culpability. It should outline the different penalties since the HITECH Act establishes different tiers for each violation.
For instance, employees should know that the maximum violation of an identical provision is $1.5 million. That’s a massive amount that no employee would want to be responsible for causing.
The module should highlight all revisions of the Act. This includes updates like the penalties involved with breaches unknown to the covered entity.
HIPAA Omnibus Final Rule
Once an employee takes training regarding the HITECH Act, they should also understand the Omnibus Final Rule. The purpose of this Rule is to strengthen existing privacy and security measures established within the HITECH Act.
The Rule also made business associates and subcontractors directly liable for their compliance with HIPAA. In turn, they would be responsible if they caused a HIPAA violation.
Patient Rights
The Privacy Rule addresses patient rights to their data, as I mentioned before. However, it can still be helpful to have a module specifically dedicated to the rights of the patient, especially if your organization deals with patients’ medical records.
After all, each of the rules within HIPAA has so many complex standards, so having modules that go over each specific part helps make them more clear.

To refresh your employees’ memories, reiterate that the Privacy Rule gives patients the right to:
- Examine their health records
- Request a copy of their records
- Direct a covered entity to transmit their PHI electronically to a third party
- Request a covered entity to make changes to a record
This module would serve as a reminder of how to handle privacy notices and what to do with patient requests.
HIPAA Disclosure Rules
Another concept to reiterate are the disclosure rules.
These apply to all employees, no matter their role within the entity. Your organization should administer a module that covers these alongside the Privacy and Security Rule modules since they go hand in hand.
A covered entity may share PHI when required to disclose the information by law. When they share this data, they must do so in a way that complies with HIPAA’s regulations. Additionally, employees must know that disclosures are permissible in response to a(n)…
- Order of the court or administrative tribunal
- Subpoena
- Discovery request
- Other situations that need disclosures for judicial or administrative proceedings
The law also permits disclosing PHI in situations of a serious or imminent threat to the health and safety of a person/the public. In these situations, a covered entity may share a person’s information without their consent if they believe that the disclosure is necessary to lessen or prevent the threat.
At the same time, the provider needs to make reasonable efforts to limit the PHI disclosed to the least amount necessary while still attempting to reduce the threat.
Because there are scenarios where sharing someone’s PHI is or isn’t allowable by the law, it’s useful to cover this specific topic as a training module.
After all, knowing this information is one of HIPAA’s requirements for employees, so you want to cover the topic in depth so that they know when to share PHI and who they can share it with.
HIPAA Violation Consequences
HIPAA violations can have severe consequences for patients, organizations, and employees. That’s exactly why you need training in the first place.
These consequences are different for civil cases versus criminal cases. A module covering the specifics of these punishments will reinforce the importance of all the topics within HIPAA. You should explain the consequences for both types of cases that I just mentioned.
Four distinct categories separate the different types of civil penalties associated with a breach.
Tier 1 is a violation that the covered entity was unaware of at the time of the breach. In other words, the breach was unintentional and the entity couldn’t have realistically avoided it. In addition, the covered entity took a reasonable amount of effort to remedy the situation and abide by HIPAA Rules.
The minimum penalty for a Tier 1 violation is $100, and the maximum is $50,000. The maximum penalty per year is around $1.5 million when adjusted for inflation.
Tier 4 is the most severe and involves willful neglect that was not corrected within 30 days of the breach. The minimum and maximum penalty per violation are $50,000 and $1.5 million, respectively.
Criminal violations are a little different, so employees should understand the consequences for these as well. There are three categories of penalties regarding criminal HIPAA violations.
The first tier shows that an individual had reasonable cause or no knowledge of the violation. Thus, it’s the least severe. Tier 2 involves someone obtaining PHI under false pretenses. And Tier 3 involves someone obtaining PHI for personal gain or with malicious intent.
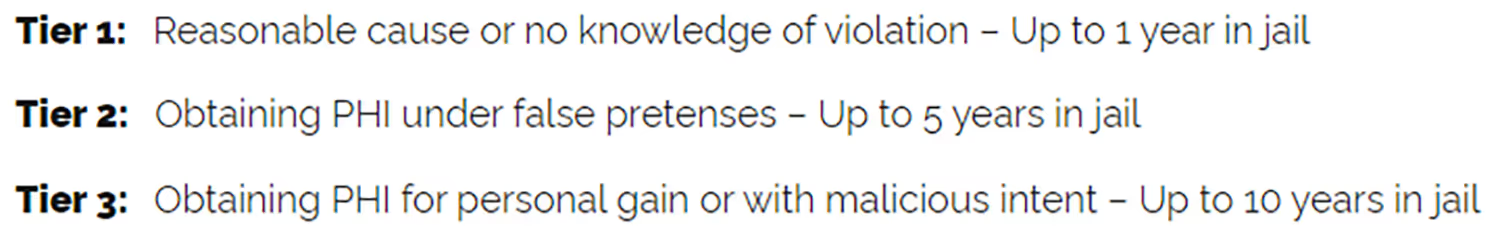
All of these categories involve time in prison. Jail time can be anywhere between a few months to up to 10 years. Because of the severity of these consequences, employees must know the potential outcomes of not following HIPAA.
Preventing HIPAA Violations and Continuing Compliance
Many organizations implement yearly regimens to comply with HIPAA laws. But you don’t need to wait a year to revisit these topics. It wouldn’t hurt to provide a refresher around halfway through the year.
This should serve as a reminder of how to prevent HIPAA violations. Topics for this part could include…
- A brief overview of the laws protecting PHI
- How to be compliant with the HIPAA laws
- General good practices to have as a healthcare employee
- The consequences of violations
The focus of this can be on explaining what the law is and best practices for employees to avoid breaches. This is also a good time to remind them how to report a violation so that you can address the issue before it becomes worse.
Addressing specific roles and responsibilities can make this refresher more effective. For instance, frontline workers have a very different daily routine compared to administrative office workers. Therefore, separate modules that focus on employee behavior can benefit your organization.
Conclusion
Every organization that deals with healthcare data must implement some form of HIPAA training.
Otherwise, employees will have no idea how to follow the law and prevent breaches.
The HHS outlines many standards that any covered entity or business associate needs to abide by. Even though the HHS requires training, it doesn’t specifically outline what information to include.
All healthcare employees have been through some sort of HIPAA training, but some of these programs may fall short since the law is vague about important topics. If employees miss important details, then they won’t be as prepared to follow the laws.
Because of this, you need to make sure that you cover all regulations to meet the HIPAA training requirements for employees.
This will allow them to learn exactly how to protect patient data and prevent a breach while also understanding potential penalties if a violation did occur.
Since the law involves so much information, it’s useful to break up the material into its own sections. This will help them better retain what they learned so they aren’t overwhelmed by so many details at once. Besides having modules on each specific HIPAA Rule, you can also provide a general overview that revisits the main topics more frequently than annually.
By following these steps and including each of these topics, your organization is on its way to meeting HIPAA training requirements for employees.
Once you establish this proper training program, you can then focus on making it more engaging so your team is even more likely to understand and follow HIPAA regulations.
Emphasize your product's unique features or benefits to differentiate it from competitors
In nec dictum adipiscing pharetra enim etiam scelerisque dolor purus ipsum egestas cursus vulputate arcu egestas ut eu sed mollis consectetur mattis pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus mauris aliquam ornare nisl purus at ipsum nulla accumsan consectetur vestibulum suspendisse aliquam condimentum scelerisque lacinia pellentesque vestibulum condimentum turpis ligula pharetra dictum sapien facilisis sapien at sagittis et cursus congue.
- Pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus.
- Justo urna nisi auctor consequat consectetur dolor lectus blandit.
- Eget egestas volutpat lacinia vestibulum vitae mattis hendrerit.
- Ornare elit odio tellus orci bibendum dictum id sem congue enim amet diam.
Incorporate statistics or specific numbers to highlight the effectiveness or popularity of your offering
Convallis pellentesque ullamcorper sapien sed tristique fermentum proin amet quam tincidunt feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
Use time-sensitive language to encourage immediate action, such as "Limited Time Offer
Feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
- Pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus.
- Justo urna nisi auctor consequat consectetur dolor lectus blandit.
- Eget egestas volutpat lacinia vestibulum vitae mattis hendrerit.
- Ornare elit odio tellus orci bibendum dictum id sem congue enim amet diam.
Address customer pain points directly by showing how your product solves their problems
Feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
Vel etiam vel amet aenean eget in habitasse nunc duis tellus sem turpis risus aliquam ac volutpat tellus eu faucibus ullamcorper.
Tailor titles to your ideal customer segment using phrases like "Designed for Busy Professionals
Sed pretium id nibh id sit felis vitae volutpat volutpat adipiscing at sodales neque lectus mi phasellus commodo at elit suspendisse ornare faucibus lectus purus viverra in nec aliquet commodo et sed sed nisi tempor mi pellentesque arcu viverra pretium duis enim vulputate dignissim etiam ultrices vitae neque urna proin nibh diam turpis augue lacus.