Defining How Often HIPAA training Needs to Take Place
Like many things within the HIPAA laws, the frequency of training is up to interpretation. But, let’s nail down how often HIPAA training needs to occur.
You want your staff to handle protected health information (PHI) safely and legally. Unfortunately, people tend to forget some of the details about how to stay HIPAA compliant. That’s why healthcare entities administer training.
But how often does HIPAA training need to take place?
The Privacy Rule and the Security Rule are two of the best-known HIPAA safeguards. Yes, there are other laws like the HITECH Act and the Final Omnibus Rule. However, many employees are first introduced to HIPAA through the Privacy and Security training modules.
As such, covered entities need to implement training so that employees can meet HIPAA’s training requirements. Training also helps minimize human error that may lead to a breach.
By implementing training, you can save your practice from paying thousands or millions of dollars in fines. If you don’t implement training, employees could face jail time if the breach they cause is serious enough.
Like many things within the HIPAA laws, the frequency of training is up to interpretation. But, let’s nail down how often HIPAA training needs to occur.
HIPAA Policies and Procedures
To properly protect PHI, upper management personnel need to implement security measures. This includes…
- The physical security of a facility that contains PHI
- Good cybersecurity practices so that no one steals digital files containing health information
- Unacceptable behavior that may compromise the privacy of the sensitive information
- Administrative procedures for reporting a breach in security
Of course, many other security measures can help protect PHI. The Privacy Rule and Security Rule are two HIPAA safeguards that concern themselves with protecting data.
Both the Privacy Rule and Security Rule discuss some policies and procedures that touch every part of the organization. They discuss how employees should handle PHI, what constitutes a breach, and what kind of safeguards a business should implement to avoid breaches.
You can find the HIPAA regulations under section 45 CFR 164.530(i)(1), titled “Standard: Policies and Procedures”.
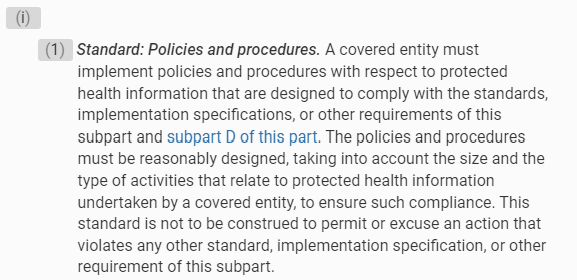
Under this section, the law states that a covered entity must implement policies and procedures to protect every aspect of the covered entity. An organization should first focus on the operations that handle PHI since these are the areas that are most vulnerable to a HIPAA violation.
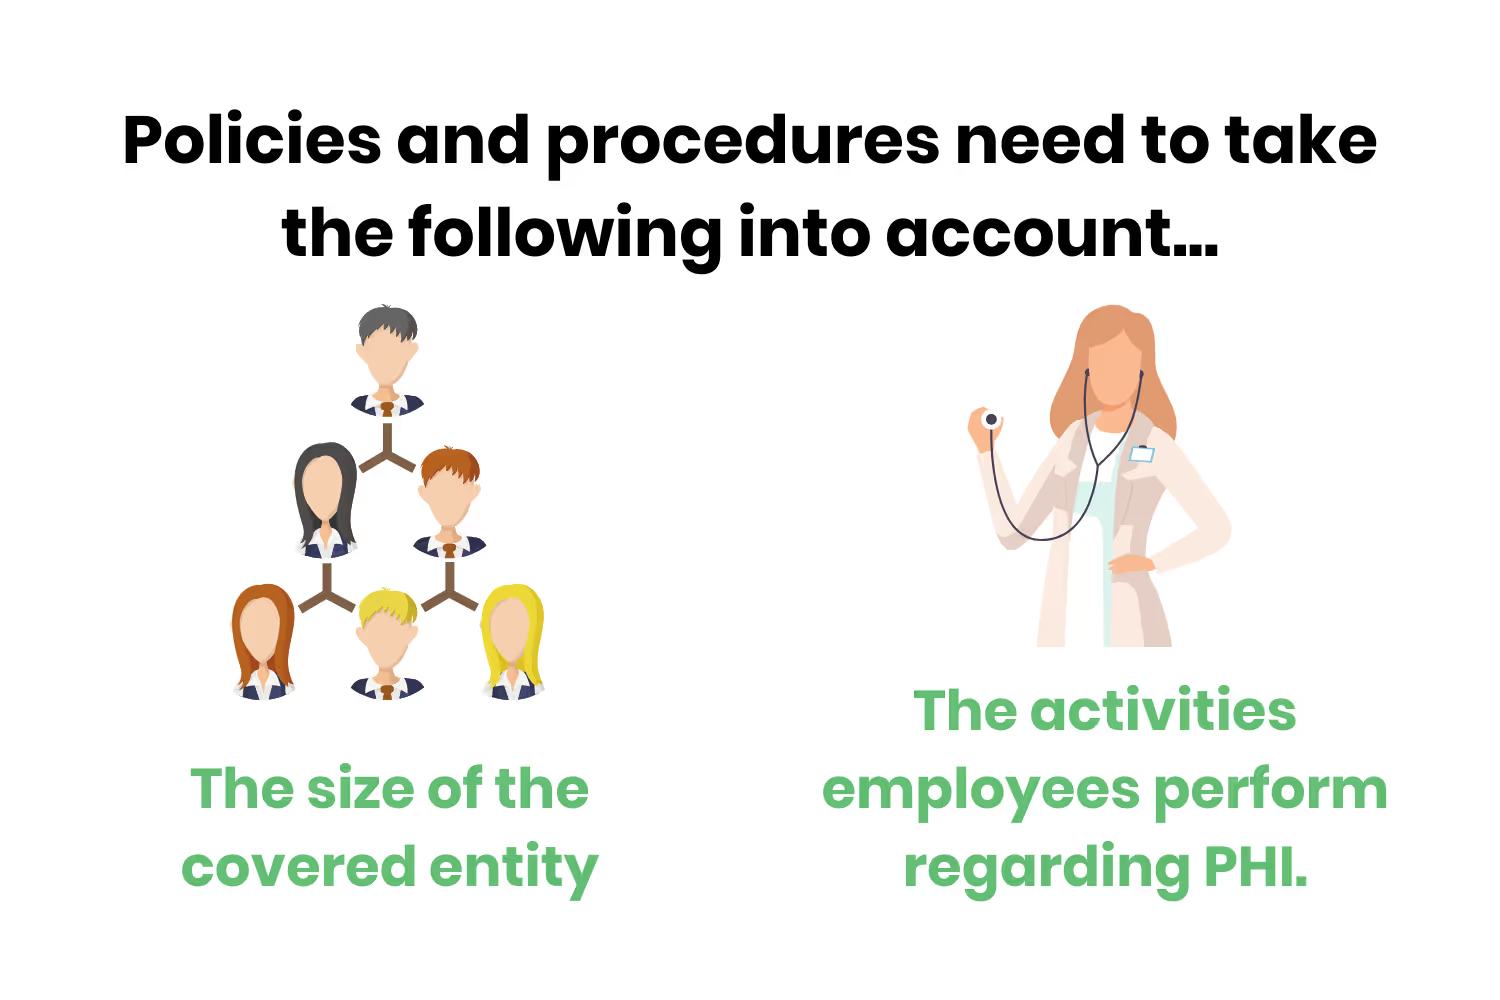
When creating the policies and procedures, the covered entity needs to factor in its size. It also needs to consider the type of activities an employee has to perform that relate to handling PHI. By looking at all of the things employees need to do to complete their jobs, the covered entity can ensure compliance.
I need to mention here that this is not a failsafe.
Just because your practice has a handbook outlining all of the ways they should and shouldn’t handle PHI doesn’t mean that you follow the rules 100% of the time. Therefore this section of the HIPAA laws doesn’t guarantee compliance.
In addition, a healthcare practice shouldn’t use this section to allow or excuse an action that may actually violate HIPAA.
Now that you have a basic understanding of how HIPAA affects the different aspects of a covered entity, we can now establish what it says about training and how often it should take place.
Privacy Rule Training
Part of the Privacy Rule highlights training in section 45 CFR 164.530(b)(1). In this section, the law lists how often the training should take place.
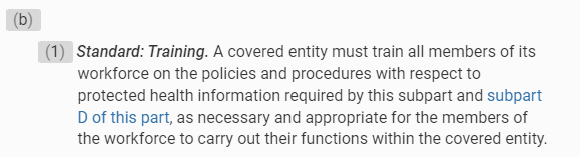
A covered entity needs to provide training to all of its employees, but especially to those who handle PHI. Furthermore, any training administered should be relevant to an employee’s role and function within the covered entity.
Everything is straightforward so far. But here is where things get tricky…
When a healthcare entity hires a new person, they need to train the new hire “within a reasonable period of time” after their start date. This is very vague and is open to interpretation. So, what would an auditor deem as a “reasonable” period of time?

Many companies interpret this to mean that they should administer training about the Privacy Rule to newly hired employees within 30 days of starting. Others believe that they should give the training at least one week before the new employee handles any PHI.
But that’s not all. There are more vague timelines regarding Privacy Rule training.
You should re-administer training within a “reasonable period of time” after a material change goes into effect. This is especially true if the change affects a member’s function while working for the covered entity.
In this specification, we again see the term “reasonable”. Many organizations that make their own HIPAA training need to update the modules whenever the government makes changes to the law. This takes time, so the new training could take a few months to administer. Depending on an auditor’s definition of ‘reasonable’, several months may not be soon enough.
Security Rule Training
The Security Rule is a bit more straightforward about what the training should cover. 45 CFR 164.308(a)(5) discusses security awareness training.

Any and all members of a covered entity’s workforce need to take training regarding the Security Rule. This is especially true for management and executives. After all, they’re responsible for creating the security standards and making sure to resolve any breaches, so they don’t happen again.
The Security Rule gives several specifications for implementation.
The training needs to cover…
- Reminders for any and all periodic security updates
- Procedures for detecting, reporting, and guarding against malicious software
- Procedures for monitoring log-in attempts
- How to report discrepancies in log-in attempts
- Procedures for creating and changing passwords as a means to safeguard them
You might notice that the Security Rule doesn’t give a timeframe of how often you should administer training.
It basically implies that a healthcare organization should have ongoing training about the topic. A covered entity should administer it whenever there’s a change in the practice's administration, such as a new service or product. They should also implement it whenever there’s a technological change.

A covered entity should implement regular risk assessments. These assessments should tell a provider whether or not the organization needs more frequent training.
Of course, as I alluded to earlier…if a change to the rules or guidelines issued by the Department of Health and Human Services (HHS), training needs re-administered and updated.
Good Practices When Determining Frequency of Training
There are some things you can do to help make sure you stay compliant.
Many healthcare organizations administer a full training program once a year and provide certificates of completion.
But should you give hours and hours of training each time there is an update to the law or an internal protocol change? Not necessarily.
A healthcare entity should use mini-training modules to help teach staff about updates to the law and any policy changes.
Below are some things you can do to help determine when you should give your staff a mini-training session…
- You can monitor the HHS website and other state publications. This monitoring can help you stay ahead of rule changes so you can prepare for the change. The best way to do this is to subscribe to the HHS news feed or other official communication channels.
- When the government issues new rules and guidelines, your organization should perform an internal risk assessment. This assessment will determine where some of the weak spots might be within your organization. The mini-training module should cover any changes you make to address these weak spots.
- Speaking of risk assessments, these can help identify how material changes in policies or procedures can affect compliance. You should make sure that any changes that may increase the risk of HIPAA violations are properly addressed. After making changes, you will need to administer a mini-training module to notify all of your staff members about the update.
- You should communicate with your human resources department to receive notices of any proposed changes. This active stream of communication can help determine whether changes to the HIPAA Privacy rule will impact compliance.
- You should also communicate with all of the IT managers working for the covered entity. With this open line of communication, you will be able to receive advanced notice of hardware or software upgrades. These changes may impact compliance and will therefore lead to training updates.
- A HIPAA refresher program can also be of use. You can administer this type of training module annually to offset the normal, more rigorous training module. That means your employees get training at least every six months.
These are just a few ways that you can be proactive when dealing with HIPAA training. You need to stay ahead of the HIPAA curb. By being vigilant and looking out for updates internally and externally, you can prevent breaches and violations from happening to you.
Conclusion
How often does HIPAA training need to take place? Like many things outlined in the HIPAA laws, the training requirements are fuzzy.
The Privacy Rule says that a covered entity should administer training on the topic when its business functions become affected by a change in the company’s policies and procedures. A new employee should complete the training within “a reasonable period of time.” Different organizations interpret the term ‘reasonable’ in a variety of ways. As long as an auditor agrees that you are compliant with the law, use your best judgment.
The Security Rule only implies how often a covered entity should administer the training. It doesn’t directly say how often an employee should take the training or how soon after starting to work for the covered entity. The Rule does imply that the training should be ongoing.
Regardless of how often employees take the training, they should take it at least once a year. Implementing regular training courses can help protect PHI. Your employees are less likely to violate the laws.
The Privacy Rule and the Security Rule are some of the most important components of HIPAA. Therefore, employees should take and complete training modules about these topics several times a year.
Emphasize your product's unique features or benefits to differentiate it from competitors
In nec dictum adipiscing pharetra enim etiam scelerisque dolor purus ipsum egestas cursus vulputate arcu egestas ut eu sed mollis consectetur mattis pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus mauris aliquam ornare nisl purus at ipsum nulla accumsan consectetur vestibulum suspendisse aliquam condimentum scelerisque lacinia pellentesque vestibulum condimentum turpis ligula pharetra dictum sapien facilisis sapien at sagittis et cursus congue.
- Pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus.
- Justo urna nisi auctor consequat consectetur dolor lectus blandit.
- Eget egestas volutpat lacinia vestibulum vitae mattis hendrerit.
- Ornare elit odio tellus orci bibendum dictum id sem congue enim amet diam.
Incorporate statistics or specific numbers to highlight the effectiveness or popularity of your offering
Convallis pellentesque ullamcorper sapien sed tristique fermentum proin amet quam tincidunt feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
Use time-sensitive language to encourage immediate action, such as "Limited Time Offer
Feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
- Pharetra curabitur et maecenas in mattis fames consectetur ipsum quis risus.
- Justo urna nisi auctor consequat consectetur dolor lectus blandit.
- Eget egestas volutpat lacinia vestibulum vitae mattis hendrerit.
- Ornare elit odio tellus orci bibendum dictum id sem congue enim amet diam.
Address customer pain points directly by showing how your product solves their problems
Feugiat vitae neque quisque odio ut pellentesque ac mauris eget lectus. Pretium arcu turpis lacus sapien sit at eu sapien duis magna nunc nibh nam non ut nibh ultrices ultrices elementum egestas enim nisl sed cursus pellentesque sit dignissim enim euismod sit et convallis sed pelis viverra quam at nisl sit pharetra enim nisl nec vestibulum posuere in volutpat sed blandit neque risus.
Vel etiam vel amet aenean eget in habitasse nunc duis tellus sem turpis risus aliquam ac volutpat tellus eu faucibus ullamcorper.
Tailor titles to your ideal customer segment using phrases like "Designed for Busy Professionals
Sed pretium id nibh id sit felis vitae volutpat volutpat adipiscing at sodales neque lectus mi phasellus commodo at elit suspendisse ornare faucibus lectus purus viverra in nec aliquet commodo et sed sed nisi tempor mi pellentesque arcu viverra pretium duis enim vulputate dignissim etiam ultrices vitae neque urna proin nibh diam turpis augue lacus.